Applies To: Cloud-managed Fireboxes, Locally-managed Fireboxes
Some of the features described in this topic are available only to participants in the WatchGuard Cloud Beta program. If a feature described in this topic is not available in your version of WatchGuard Cloud, it is a beta-only feature.
To manage a Firebox configuration from WatchGuard Cloud, you must add the Firebox to WatchGuard Cloud as a cloud-managed device. You can manage a cloud-managed Firebox from WatchGuard Cloud only.
When you add a cloud-managed Firebox, you create a new configuration in WatchGuard Cloud through one of these methods:
- Create a new configuration manually.
- Copy configuration settings from another cloud-managed Firebox in the same account.
- Import many supported settings from a Firebox .XML configuration file to help build the cloud-managed configuration. You can do this when you add the device through the Add Device Wizard, or you can use the Import Configuration wizard after you add the device. This topic describes how to use the Add Device Wizard. For information about Import Configuration wizard workflow, go to Import Configuration Settings from a Firebox Configuration File.
For information about how to change an existing Firebox from local management to cloud management, go to Change a Locally-Managed Firebox to Cloud Management.
For best practices on how to change your locally-managed Firebox to cloud management, go to the Firebox Migration to Cloud Management Guide.
Caution: Do not reset a cloud-managed Firebox to factory-default settings as a general troubleshooting step. It rarely resolves issues and breaks the WatchGuard Cloud management connection. After you reset the Firebox, the device cannot reconnect because of a WatchGuard Cloud key mismatch. Recovery might require you to remove and re-add the device to WatchGuard Cloud, which can result in the loss of configuration and logs.
Before You Begin
Before you add a Firebox to WatchGuard Cloud, make sure that:
- You have activated the Firebox in your WatchGuard account. For more information, go to Activate a WatchGuard Firebox.
- The Firebox has a valid Standard Support license (Fireware v12.9 or higher) or a current Total Security Suite or Basic Security Suite subscription.
- The Firebox is allocated to a Subscriber account (Service Providers only). For more information, go to Allocate Fireboxes.
- The Firebox is connected to the network and has reliable access to the Internet.
Your operator role determines what you can see and do in WatchGuard Cloud. Your role must have the Devices permissions to view or configure this feature. For more information, go to Manage WatchGuard Cloud Operators and Roles.
To add a Firebox as a cloud-managed device, it must meet these requirements:

For a Firebox to successfully connect to WatchGuard Cloud as a cloud-managed device, it must run Fireware v12.5.7 or higher.
The Fireware version your new Firebox was manufactured with is printed on a sticker on the Firebox packaging. The version of Fireware originally manufactured on the device also appears in the Device Information section of the Product Details page in the WatchGuard website.
If your Firebox runs a lower version of Fireware, you must first set up the Firebox as a locally-managed device and upgrade it to Fireware v12.5.7 or higher before you can add it as a cloud-managed device. The device automatically upgrades to the latest Fireware version for that device. For information about Fireware upgrade methods, go to Firebox Upgrade, Downgrade, and Migration.
If you previously configured the Firebox as a locally-managed device, you must reset it to factory-default settings before it can connect to WatchGuard Cloud as a cloud-managed device. For the steps to reset your Firebox, go to Reset a Firebox.
Add a Cloud-Managed Firebox to WatchGuard Cloud
When you add a Firebox to WatchGuard Cloud as a cloud-managed device, you configure the device name, time zone, external network settings, wireless settings, and device passwords. WatchGuard Cloud automatically configures other device settings with secure defaults.
To add a Firebox to WatchGuard Cloud as a cloud-managed device:
- Log in to your WatchGuard Cloud account.
- For Service Provider accounts, from Account Manager, select My Account.
- Select Monitor > Devices or Configure > Devices.
- Click Add Device.
A list of activated Fireboxes opens.If the device is activated but does not appear in the list, make sure the Firebox is allocated to a Subscriber account if you are a Service Provider. For more information, go to Allocate Fireboxes.
- Select the Firebox you want to add, or click
 then select Add Device.
A confirmation dialog box opens.
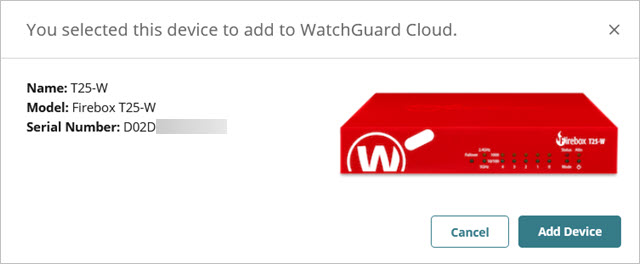
- Click Add Device.
The Add Device to WatchGuard Cloud page opens.
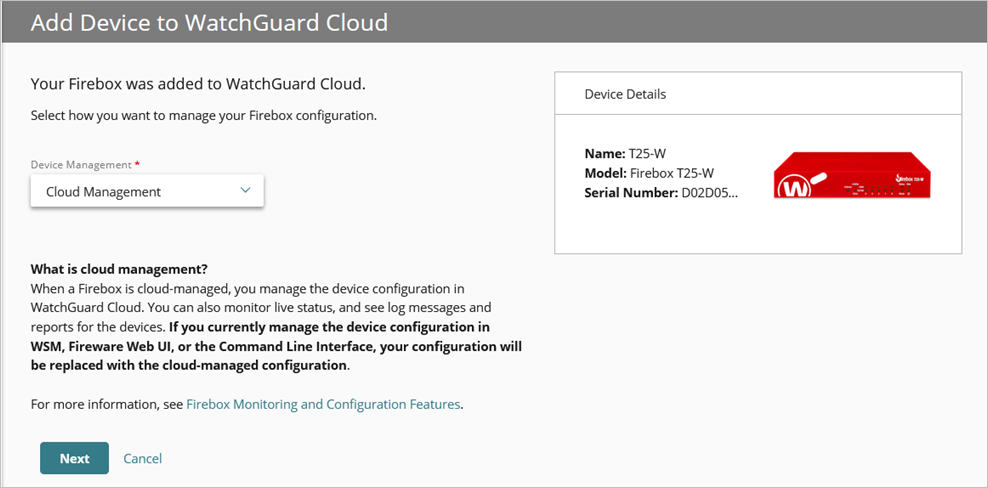
- From the Device Management drop-down list, select Cloud-Managed, then click Next.
The Cloud Management page opens. - From the Configuration Type drop-down list, select one of these configuration types:
- Create a New Configuration
- Copy a Configuration from Another Cloud-Managed Firebox
- Upload an .XML Configuration File
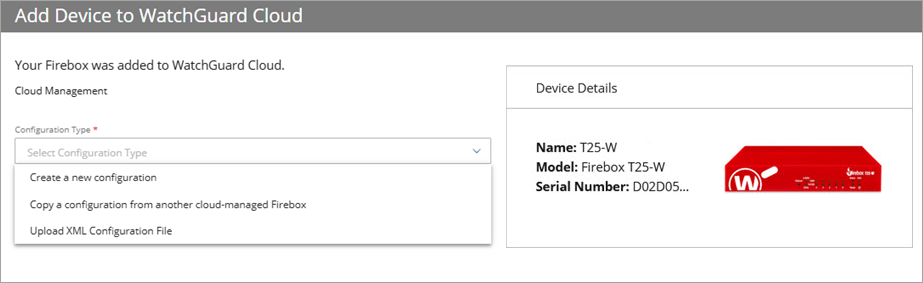
- From the Device Management drop-down list, select Cloud-Managed, then click Next.
- Select Create a New Configuration or Copy a Configuration from Another Cloud-Managed Firebox.
If you copy configuration settings from another cloud-managed Firebox, you must select the Firebox you want to copy from. The Firebox must be in the same account.
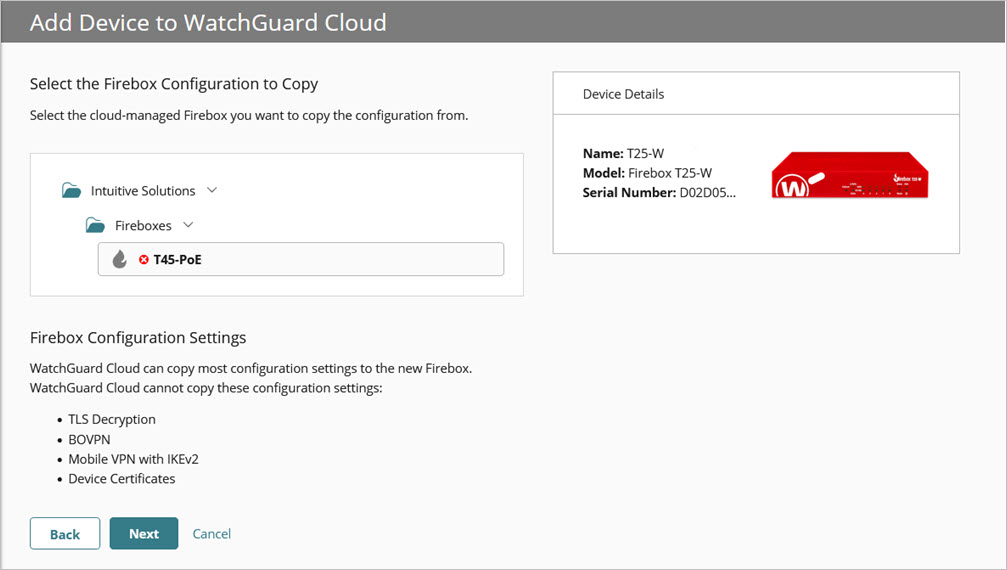
- Click Next.
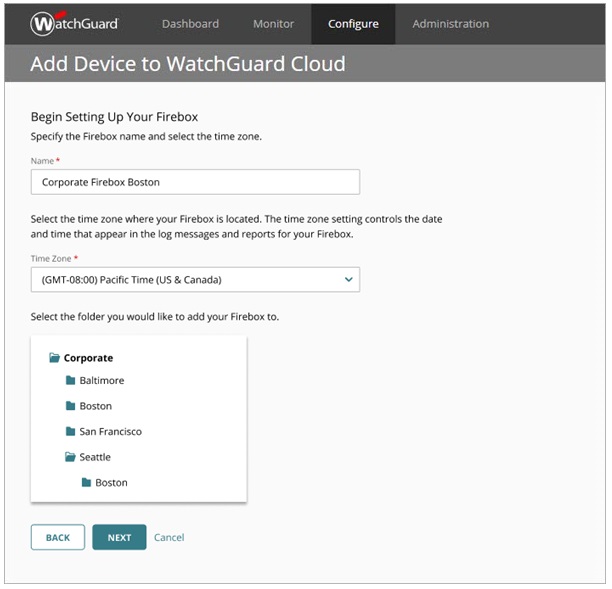
The Begin Setting Up Your Firebox page opens. - Configure Firebox system settings:
- Device Name — The name to identify the Firebox in WatchGuard Cloud.
- Time Zone — The time zone of the location where the Firebox is installed.
- From the Device Folder drop-down list, select the folder that you want to add your device to. Device Folders help you view status and summary data for groups of devices.
If you have only one root folder, the folder list does not appear.
- Click Next.
- From the Connection Type drop-down list, select an option for the Firebox external interface. Select and configure one of these options:
DHCP
Select this option to configure the Firebox to use DHCP to request an IP address on the external network.
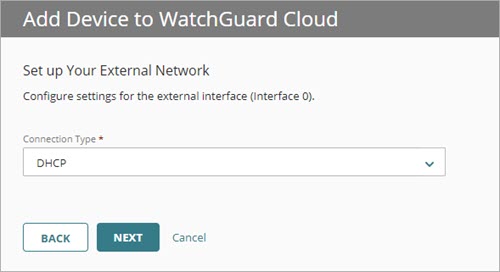
If you select DHCP, there are no other network settings to configure.
Static IP
Select this option to configure the Firebox to use a static IP address on the external network.
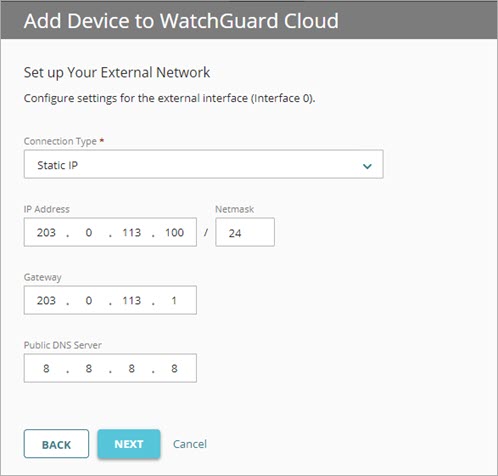
If you select Static IP, configure the Firebox external network IP address and netmask, a network gateway on the same subnet, and the IP address for a public DNS server.
PPPoE
Select this option to configure the Firebox to use PPPoE to get an IP address on the external network.
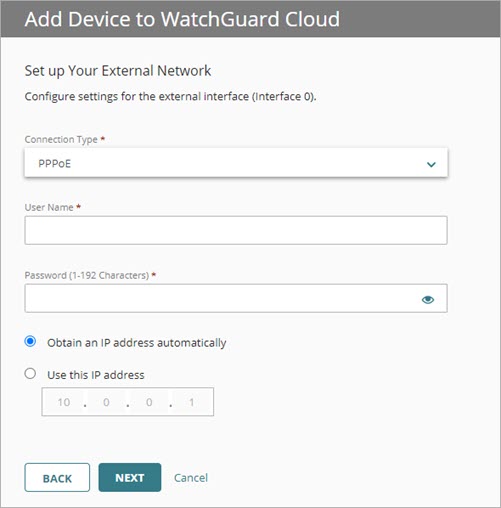
If you select PPPoE, configure the user name and password, and select whether to obtain an IP address automatically or to configure a specific IP address.
4G LTE or 5G Modem
If you have a Firebox with a 4G LTE interface module or integrated 5G modem, you can enable the cellular connection.
To establish a connection for a cellular modem, some wireless service providers require an Access Point Name (APN). To determine the requirements to configure your cellular modem, verify with your provider whether an APN is required to connect.
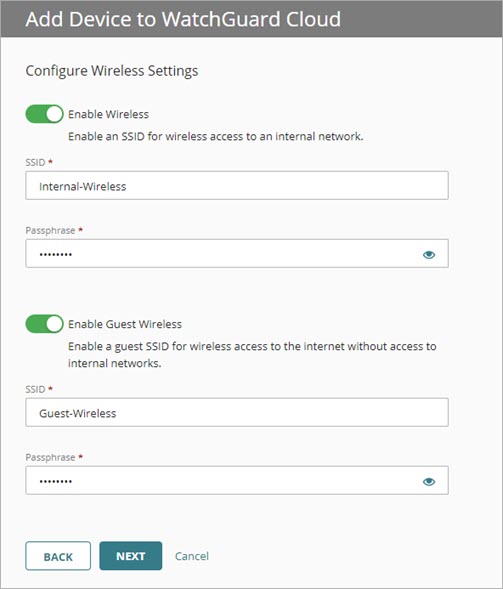
- For a wireless Firebox, you can enable wireless on the internal and guest networks.
- Enable Wireless — Enable this option to configure an SSID and passphrase for wireless connections to the internal network.
- Enable Guest Wireless — Enable this option to configure an SSID and passphrase for wireless connections to the guest network.
- Click Next.
- Set the Status and Admin user device passwords for connections to Fireware Web UI on the Firebox. Device passwords must be 8–32 characters long, and must contain uppercase and lowercase letters, at least one number, and at least one symbol. The Status and Admin passwords cannot be the same.

Caution: We recommend that you specify unique passwords for each Firebox you manage and change them frequently.
For a cloud-managed Firebox, you can use Web UI to recover the Firebox connection to WatchGuard Cloud. You cannot use Web UI to modify the Firebox configuration.
- Click Next.
- On the last page of the Add Device wizard, review the steps to connect the Firebox.
If the Firebox uses factory-default settings and you created a new configuration, the Firebox connects to WatchGuard Cloud and the new configuration deploys to it.
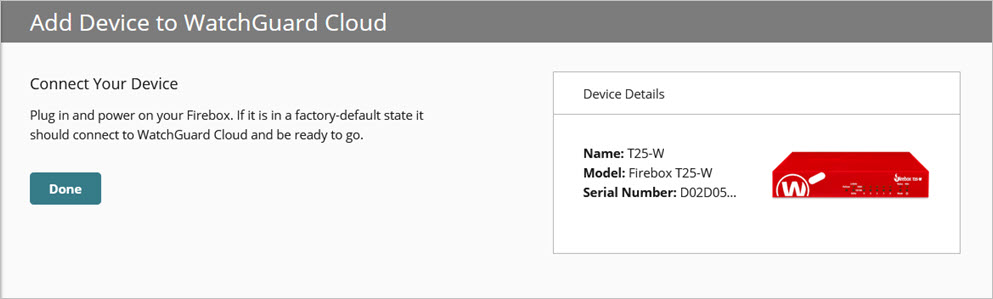
When you copy a configuration from an existing Firebox, review the additional steps you might need to complete before you deploy your configuration. WatchGuard Cloud holds the updated configuration until you deploy it to the Firebox.

If the Connection Type is Static IP or PPPoE, you must complete additional steps to configure the Firebox to connect.
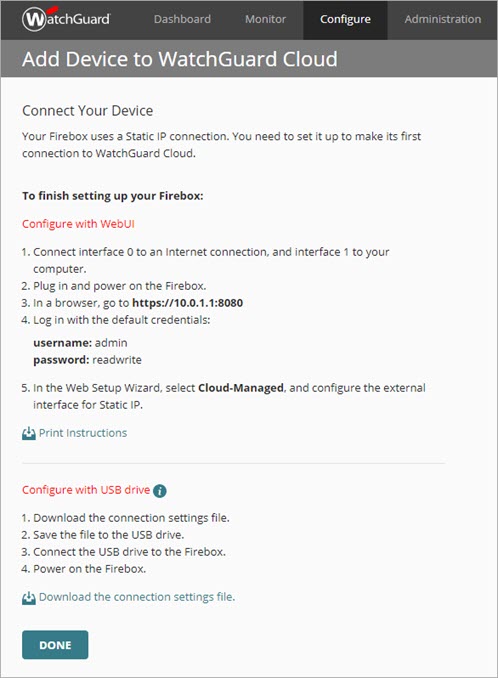
- To print the entire page of instructions, click Print Instructions.
- To download the connection settings, click Download the Connection Settings File. These requirements apply when you download the file:
- The USB drive must be formatted with the FAT, VFAT, or FAT32 file system and must be writable.
- The file must be saved as the CSV (Comma Delimited) (*.csv) file type.
For more information, go to Use a USB Drive to Configure Interface Settings.
After you add a cloud-managed Firebox, the device configuration is immediately deployed and available for the Firebox to download.
If you re-add a Firebox that you removed from WatchGuard Cloud, and if the current configuration does not include a branch office virtual private network (BOVPN), you can revert to a previous configuration version that includes a BOVPN. The BOVPN tunnel rejoins if you did not remove the BOVPN configuration on the peer endpoint Firebox. If you deployed any configuration on the peer endpoint Firebox after you removed the other Firebox, but before you re-added the other Firebox, you must deploy the configuration on the peer endpoint Firebox if you receive a message about undeployed BOVPN changes.
The availability of previous configuration versions depends on your data retention settings. For information about data retention, go to About Data Retention and Data Deletion.
If the configuration was not successfully deployed, a default name for the new device shows in the WatchGuard Cloud list of devices.
When you import a configuration from a Firebox, you can import some configuration settings from an existing Firebox configuration file to a cloud-managed Firebox configuration. Some configuration settings are not importable. For more information about how to import configuration settings, go to Import Configuration Settings from a Firebox Configuration File.
If the file contains settings that conflict with Firebox default objects such as a default alias, the Add Device wizard uses the default objects. For more information about duplicate settings, go to Import Configuration Settings from a Firebox Configuration File.
Before you import an .XML configuration file to add a cloud-managed Firebox, make sure that you have exported a valid .XML configuration file from the Firebox you are adding to WatchGuard Cloud. For more information, go to Configuration File Requirements.
You cannot use the .XML configuration import in the Add Device wizard for Firebox Cloud.
To import an .XML configuration file from another device:
- From the Device Management drop-down list, select Cloud-Managed, then click Next.
- From the Configuration Type drop-down list, select Upload an XML Configuration File.
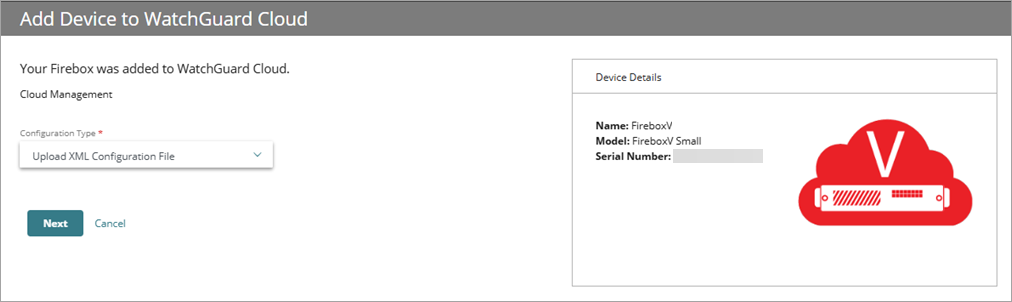
- Click Next.
- Configure these Firebox system settings:
- Device Name — The name to identify the Firebox in WatchGuard Cloud.
- Time Zone — The time zone of the location where the Firebox is installed.
- From the Device Folder drop-down list, select the folder that you want to add your device to. Device Folders help you view status and summary data for groups of devices.
If you only have only one root folder, the folder list does not appear.
- Click Next.
- Set the Status and Admin user Firebox device passwords for connections to Fireware Web UI on the Firebox. Device passwords must be 8–32 characters long, and must contain uppercase and lowercase letters, at least one number, and at least one symbol. The Status and Admin passwords cannot be the same.
Caution: To keep your device secure, make sure you do not use the default passwords for the admin account (readwrite) and status account (readonly). We recommend that you specify unique passwords for each Firebox you manage and change them frequently.
For a cloud-managed Firebox, you can use Web UI to recover the Firebox connection to WatchGuard Cloud. You cannot use Web UI to modify the Firebox configuration.
- Click Next.
The Import Configuration page opens. - Drag the .XML configuration file to the import box, or click the import box and click Browse to select the file.
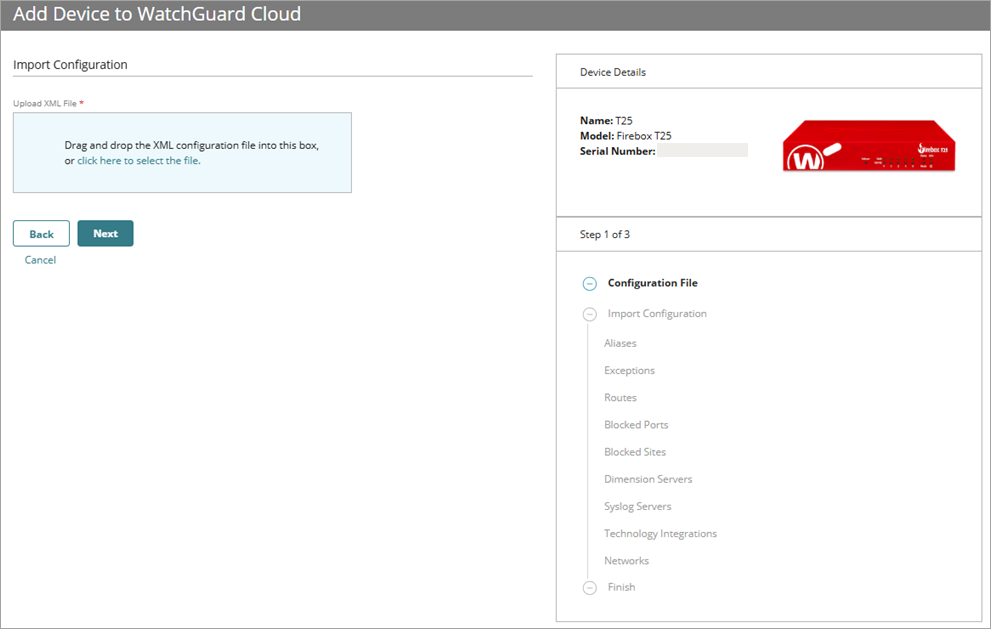
- Click Next.
The Aliases page opens.
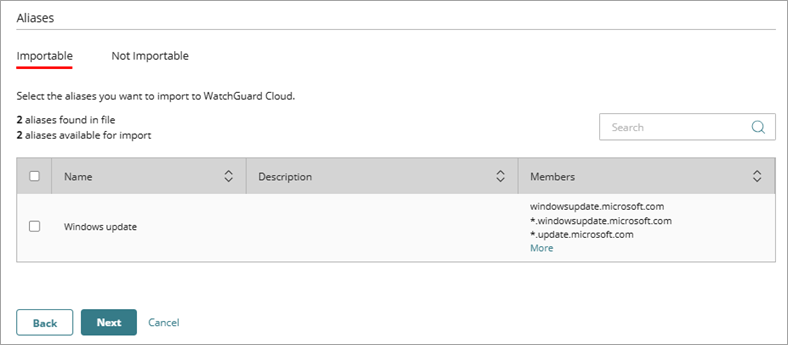
- To import an alias, select the check box next to each alias. The page shows the number of aliases available to import and the number of aliases found in the configuration file.
- Click Next.
The Exceptions page opens. - Select the check box next to each exception to import. The page shows the number of exceptions available to import and the number of exceptions found in the configuration file.
- Click Next.
The Routes page opens. - Select the check box next to each route to import. The page shows the number of routes available to import and the routing distance found in the configuration file.
- Click Next.
The Blocked Ports page opens. - Select the check box next to each blocked port to import. The page shows the number of blocked ports available to import in the configuration file.
- Click Next.
The Blocked Sites page opens. - Select the check box next to each blocked site to import. The page shows the number of blocked sites available to import and their description in the configuration file.
- Click Next.
The Dimension Servers page opens and shows the Dimension servers on the cloud-managed Firebox. - (Optional) To change the list of Dimension servers, click Select Server.
A dialog box opens and shows the list of available Dimension servers.- Select the check box next to the Dimension servers that you want to use with WatchGuard Cloud. You can select up to two Dimension servers from the list.
- Click OK.
- To prioritize Dimension servers, click the move handle for a server and drag it to a new position in the list.
- Click Next.
The Syslog Servers page opens. The list of servers includes syslog servers from both the import file and the cloud-managed configuration. - Select the check box next to each syslog server that you want to use with WatchGuard Cloud. You can select up to three syslog servers.
- Click Next.
The Technology Integrations page opens. - Select the check box next to each technology integration to import.
When you import a technology integration, it replaces an existing technology integration of the same type. For more information, go to About Firebox Technology Integrations.
- Click Next.
The Networks page opens. The page shows the number of networks available to import and the number of networks found in the configuration file.When you import a network, WatchGuard Cloud imports the network and the associated interface and network settings from the configuration file. Depending on the configuration, this can include:
- Physical, VLAN, bridge, and link aggregation (LAG) interfaces
- Internal, external, and wireless networks
- IP address and secondary network settings
- DHCP client or server settings, including DHCP reservations
- DNS and WINS settings
- MAC address control lists
- Other cloud-supported interface properties, such as MTU and link speed
You must import an entire network and the network settings. You cannot import only part of a network configuration, such as only DHCP reservations or secondary networks. The Add Device wizard does not import network settings that WatchGuard Cloud does not support. For example, loopback interfaces are not imported. The wizard also does not import SD-WAN actions, even though WatchGuard Cloud supports SD-WAN actions. Unsupported settings or settings that are not imported can appear as not importable in the Import Configuration wizard. For more information, go to Not Importable Settings.
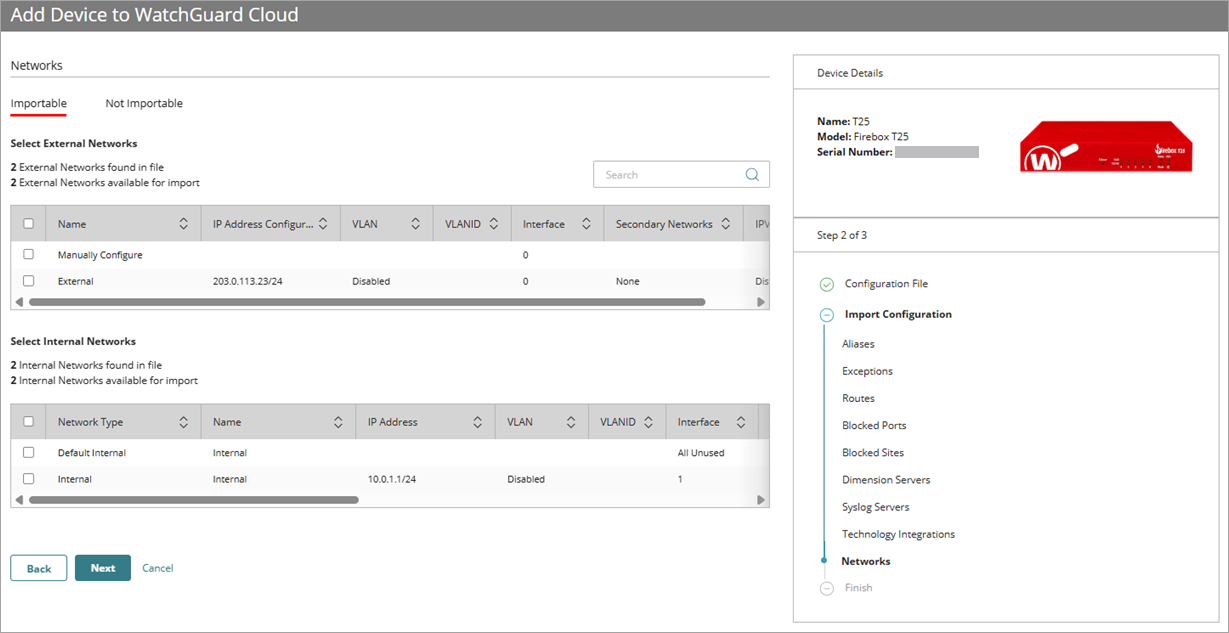
- Select the check box next to each network you want to import.
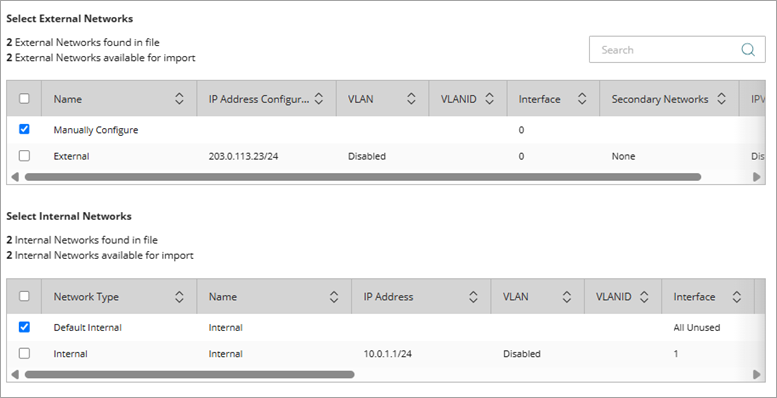
- (Optional) If you want to manually configure an external network or create a default internal network:
- To configure an external network later in the wizard, select Manually Configure.
- To create a default internal network, select Default Internal.
- If you import an Optional or Custom network from a locally-managed Firebox configuration, the Import Configuration wizard prompts you to select a different network type.
WatchGuard Cloud does not support Optional or Custom network types. If the configuration file includes an Optional or Custom network, select Internal or Guest as the network type for the cloud-managed configuration.
To select a different network type, from the Optional or Custom drop-down list, select Internal or Guest.

- Click Next.
The Finish page opens.
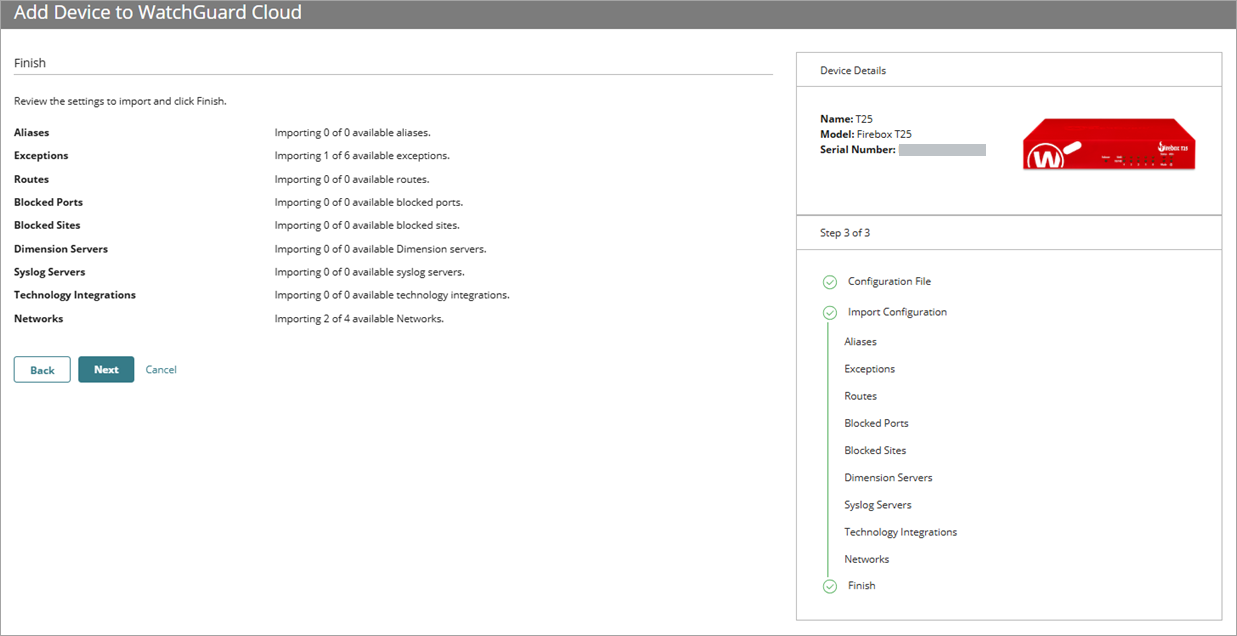
- Click Next.
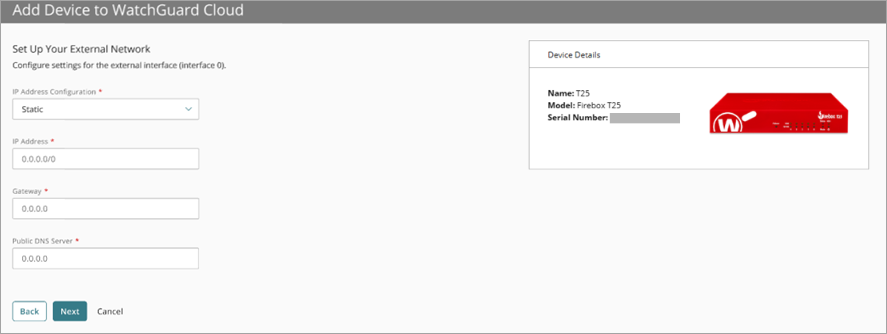
- If you did not import an external network, configure an external network manually. From the IP Address Configuration drop-down list, select Static, DHCP, or PPPoE, then complete the settings. For more information, go to Select External Interface Connection Type.
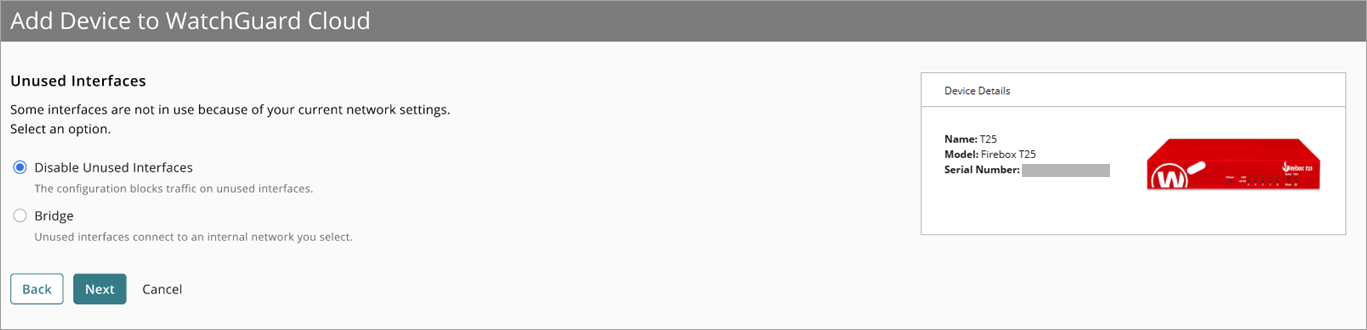
- If the imported XML configuration contains unused interfaces, select how to handle them. By default, Disable Unused Interfaces is selected.
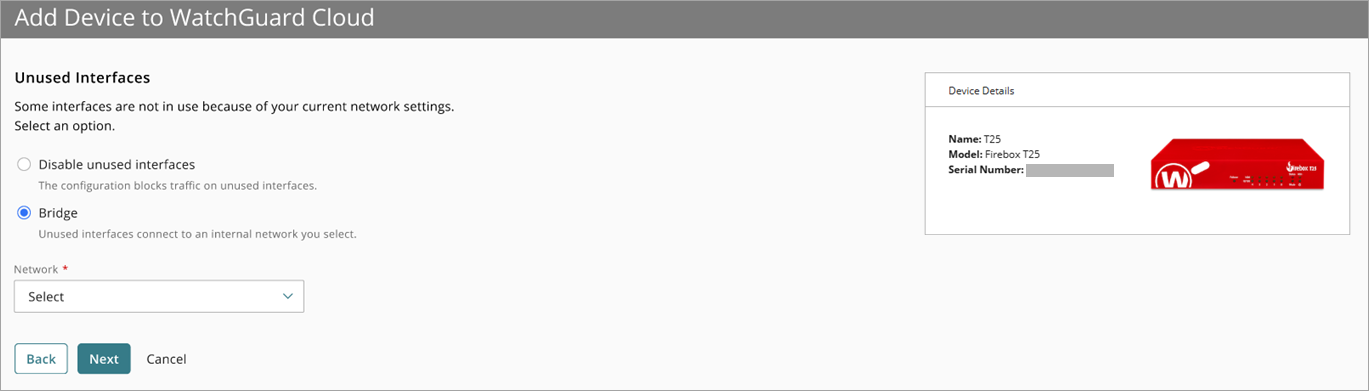
If you select Bridge, a drop-down list opens with all networks currently associated with the configuration. Select the network to which you want to bridge the unused interfaces.
- Click Next.
The Finish page opens.
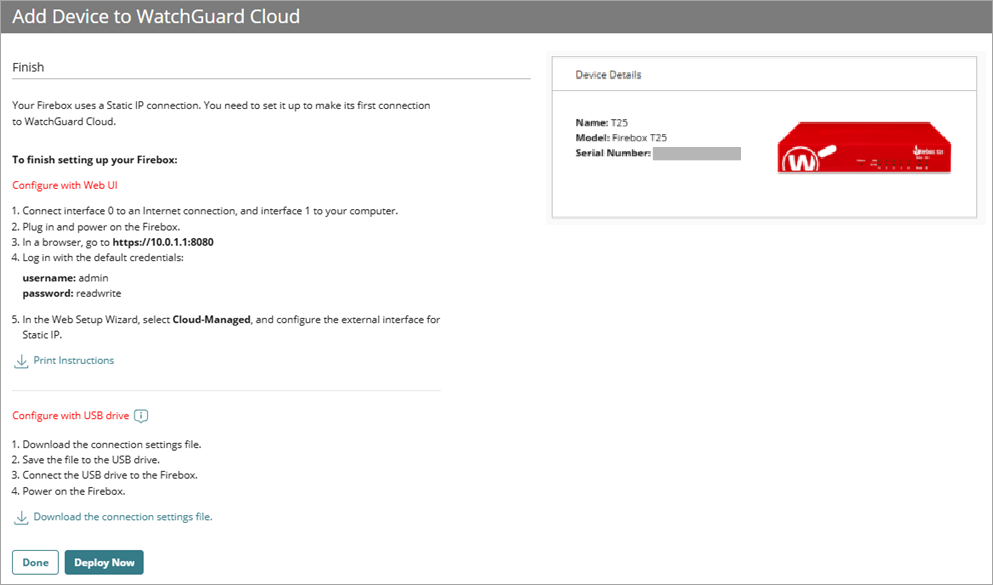
- Click Done to stage your changes, or click Deploy Now to deploy the changes immediately.
Firebox Default Configuration Settings
The initial configuration for a cloud-managed Firebox includes these settings:
Networks:
- External (Interface 0) — IP address settings you configured
- Internal (all other interfaces, bridged) — IP address 10.0.1.1/24
- Guest (wireless, if supported and enabled) — IP address 10.0.1.2/24
Policies:
- Outgoing — Allows outbound TCP, UDP, and Ping connections from the internal network to the external networks
- Guest — Allows outbound TCP, UDP, and Ping connections from guest networks
Security Services:
- Security Services are enabled in the default policies
After you add the cloud-managed Firebox, you can edit the configuration and deploy the updated configuration for the Firebox to download.
Connect the Firebox
Connect the Firebox to a network with reliable Internet access. The steps to set up and connect the Firebox depend on how the Firebox gets an IP address for the external interface.
To connect a Firebox that can use DHCP to get an IP address:
- Connect interface 0 to the network.
- Start the Firebox with factory-default settings.
The Firebox automatically tries to connect to WatchGuard Cloud to download its configuration.
For steps to reset the Firebox to factory-default settings, go to Reset a Firebox.
If your Firebox cannot get an address through DHCP, you can use the Web Setup Wizard to configure connection settings, or you can use the connection settings file.
To use the Web Setup Wizard:
- Connect Firebox interface 0 to a network with Internet access.
- Start the Firebox with factory-default settings.
- Connect Firebox interface 1 to your computer.
- Open a web browser and go to https://10.0.1.1:8080.
- Log in with the user name admin and the passphrase readwrite.
- Select Cloud-Managed as the configuration method.
- Configure external network settings required for the Firebox to connect to your network.
The Firebox uses these settings to connect to the local network, and then connects to WatchGuard Cloud to download its configuration.
For information about how to use the connection settings file to set up your Firebox, go to Use a USB Drive to Configure Interface Settings.
Automatic Fireware Upgrade
The minimum version of Fireware required for WatchGuard Cloud to deploy a configuration might be higher than the version currently installed on the Firebox. The minimum Fireware version required for cloud management is Fireware v12.5.7 (M Series) or Fireware v12.6.4 (T Series).
The first time the Firebox connects, WatchGuard Cloud determines whether your Firebox requires an upgrade before it can download the configuration. If an upgrade is required (for example, v12.5.4 to v12.5.6 or v12.6.1 to v12.6.3), WatchGuard Cloud automatically upgrades the Firebox to the latest Fireware version for cloud management. After the upgrade is complete, the Firebox connects to WatchGuard Cloud to download the configuration.
Verify the Firebox Status
After you connect the Firebox, verify the Firebox connection status and other summary information on the Device Summary page and Live Status page.
For more information, go to:
About the WatchGuard Cloud User Interface
Recover the Firebox Connection to WatchGuard Cloud
Add FireboxV to WatchGuard Cloud (Cloud-Managed)
Add Firebox Cloud to WatchGuard Cloud (Cloud-Managed)
(Video) Cloud-Managed Firebox: Configuration Overview